Experts talk new rules and compliance approaches in Q4 2026
Photo: Getty Images
By Julie DiMauro | October 26, 2026 | Follow GRIP on LinkedIn
https://www.linkedin.com/showcase/global-relay-intelligence-and-practice/home/
A few of GRIP’s legal and compliance expert sources shared their thoughts on AI, prediction markets, and reaching out to the regulators.
In 2026, the SEC has unleashed a wave of proposed rulemaking that could redesign the regulatory landscape and compel changes to compliance programs. From the “retailization” of the private marketplace to the possible elimination of the pay-to-play rule and potential for less frequently mandated SEC reporting, the emphasis right now is on tracking these developments as we await their final formats.
I asked several legal and compliance pros to consider what regulatory and general compliance topics linger most on their clients’ minds and what they are advising them to do in as we await new rulemaking in Q4 of 2026.
Janaya Moscony is president of SEC3 Compliance and a former SEC regulator. Lisa Detwiler is the managing director, General Counsel of FS Investment Solutions, Future Standard’s wholly owned broker-dealer subsidiary. Kwame Lewis (CFA, CPA, FCCA) is co-founder of Lewis-Levy Consulting, advising clients on investment management, particularly private equity industry and private equity fund-of-funds and endowments.
Cybersecurity and AI
AI’s capacity to supercharge cyberattacks on the one hand while providing defenders with powerful, real-time, and automated tools to neutralize threats is an interesting mix of perils and rewards. Managing the security risks of AI requires securing the AI models themselves and using AI effectively to strengthen the organization’s cyber defenses.
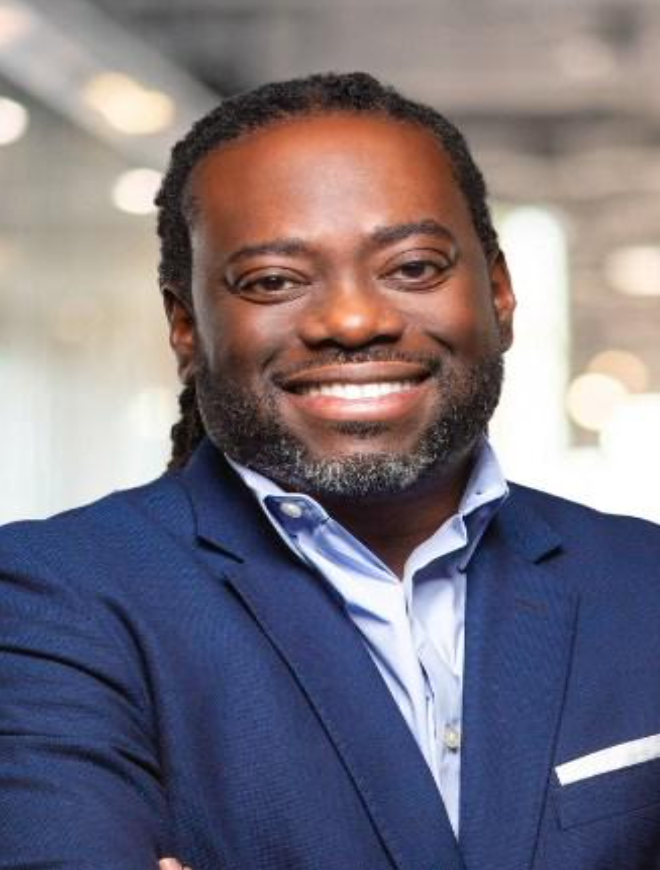
Kwame Lewis.
Photo: Lewis-Levy Consulting
“You need to know that your data is not just going into some black box; you need to know where it is and how it’s being used,” Lewis said. “The solution is not saying you won’t use the tools. That’s the wrong answer. But you need to have a compliance program that recognizes the risks.”
“And you have to keep in mind that the next wave of exams are probably going to feature questions about your compliance posture in this regard,” Detwiler said. “Examiners will want to know every function that is using AI and certainly if you are using it in the investment management process. Any cybersecurity events that have used AI need to be reported as such,” she added.
Lisa Detwiler.
Photo: Future Standard
Lewis agreed. “And businesses might not be allowing it to be used on their official channels, but they still have it running on the side devices, personal devices, and using AI tools as note-takers, etc., so this underscores the need for monitoring.”
Lewis said the compliance and legal professionals he speaks to are most concerned about scaling in this environment. Growing the technology capabilities with the right policies and procedures, then executing on them.
New and proposed rules
I asked the trio about some of the new and proposed rules coming out of the SEC and FINRA in recent months.
Janaya Moscony.
Photo: Private
“The outside business activities, or OBA, rule at FINRA is an interesting one,” Moscony said. “We generally tell the CCO that it’s a good determination for them to make whether the OBA needs to be disclosed. The CCO and firm is in the best position to judge if the outside activity is conflicting with their daily responsibilities. If it’s on the line and in a gray area, the rep should err on the side of reporting it, and then the CCO can determine whether it’s relevant or not,” she said.
Detwiler said her firm’s process is to have the manager approve any OBA before it comes to compliance, and the approval gets attached to the request that goes to compliance. “I envision we will keep that process in place,” she said, “notwithstanding the changes to the rule, but there could be some business considerations to be factored in here. This is why I have always taken the position that the direct manager needs to have a say in this,” she said.
Dealing with prediction markets
Detwiler said she recently read a study that discussed financial services businesses being all over the spectrum in terms of how and whether they are monitoring the prediction markets. “We are updating our Code of Business Conduct and Ethics to specifically outline our expectations here.”
Lewis pointed out that it is yet another strain on the compliance program budget, and Moscony said the examiners at the agencies might start to ask if firms are identifying this as a potential risk area. “It’s best for firms that are engaging these types of businesses or have confidential information that could be used inappropriately to have clearly laid-out a risk plan specific to prediction markets. As examiners become familiar with these risks and we hear about them more, they will be even more focused on the topic.”
Reaching out to the regulators
All of them said people need to be realistic about this, despite what is said at the large conferences. “They always say ‘reach out to us,’ but, no, we don’t really want to put a target on our back, thank you.” Lewis clarified that: “I mean, it might not make them run to you to do a complete examination of you, but I get why it makes people nervous.”
Some firms fear that it looks like they have a problem if they’re reaching out to the regulator, so why do it? “The compliance and legal folks I talk to reach out to their lawyers and not to the SEC if they’re already engaged in the activity. If it’s a question related to proposed rulemaking, there’s a process for that with comment letters and the like,” Moscony said.
Detwiler pointed out that US regulators push out a lot of guidance documents, alerts, no-action letters, and other documents to help them already. “And if there’s a gray area, they get a legal opinion,” Moscony reiterated. “And that’s what I’d advise, more so than going to the SEC for clarity.”
This alert is provided for informational purposes only and does not constitute legal or investment advice.
Need assistance with your compliance program? SEC3’s team of experienced compliance professionals can help. For more information, please email us at info@sec3compliance.com, call (212) 706-4029 x 214, or visit our website at www.sec3compliance.com.
SEC3 provides links to other publicly available legal and compliance websites for your convenience. These links have been selected because we believe they provide valuable information and guidance. The information in this e-newsletter is for general guidance only. It does not constitute the provision of legal advice, tax advice, accounting services, or professional consulting of any kind.
For over two decades, we have been providing compliance consulting services and servicing as outsourced Chief Compliance Officers. Our professionals have served as SEC regulators and in senior leadership, guiding the industry’s principal compliance association. Our consultants also have hands-on industry experience as chief compliance officers, experienced securities attorneys and senior management of investment advisers, broker-dealers and fund administrators.
What can SEC3 do for you?
SEC3 offers an extensive suite of customizable compliance services for investment advisers, private fund advisers, CPOs, CTAs, investment companies, institutional investors and broker-dealers which can complement your internal compliance program on a one-time or recurring basis depending on your needs.
Call us today at (212) 706-4029 x 214, or shoot us an email at info@SEC3compliance.com so we can set up a time for one of our consultants to discuss your needs and how we can help.